Before you begin
- You need Admin access to your Tamarind organization.
- You need admin access to your identity provider (for example, the Okta Admin Console, Microsoft Entra admin center, or Google Admin console).
- Every user who should get access needs an email address on your company domain set in the IdP.
Setting up SSO doesn’t change how anyone signs in until Tamarind activates it. You can configure and test safely.
1. Open Organization settings
Sign in at app.tamarind.bio/app. In the left sidebar, click Organization (1).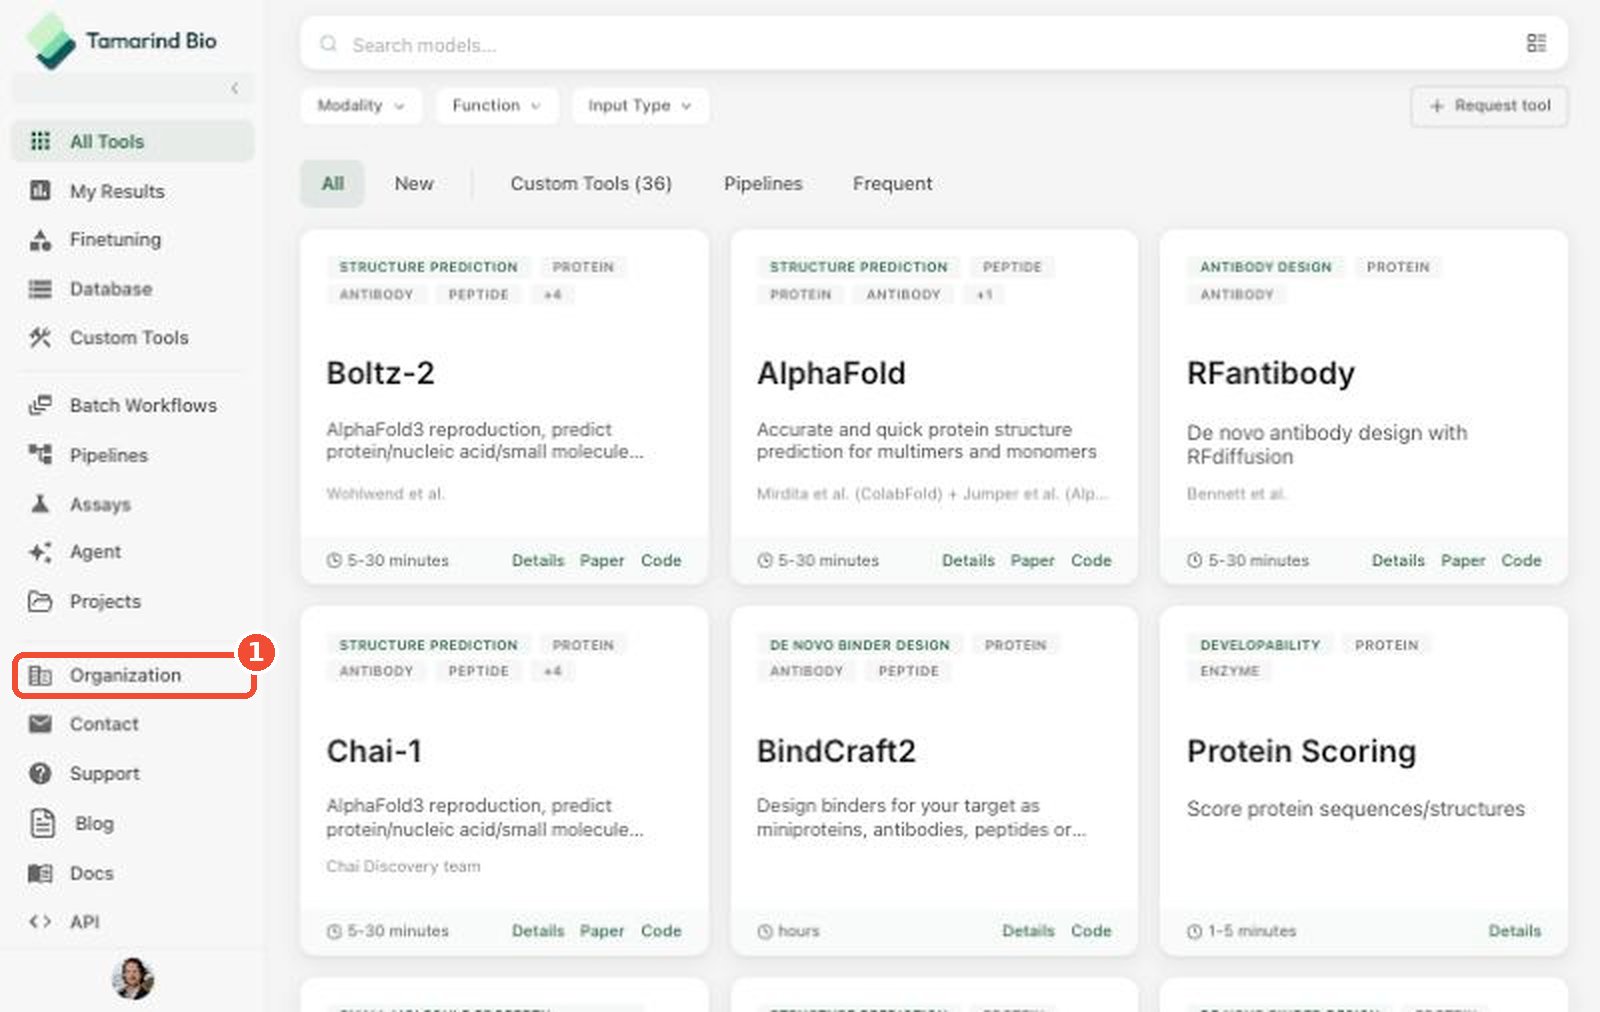
2. Open Single Sign-On
Under Organization in the settings menu, click Single Sign-On (1).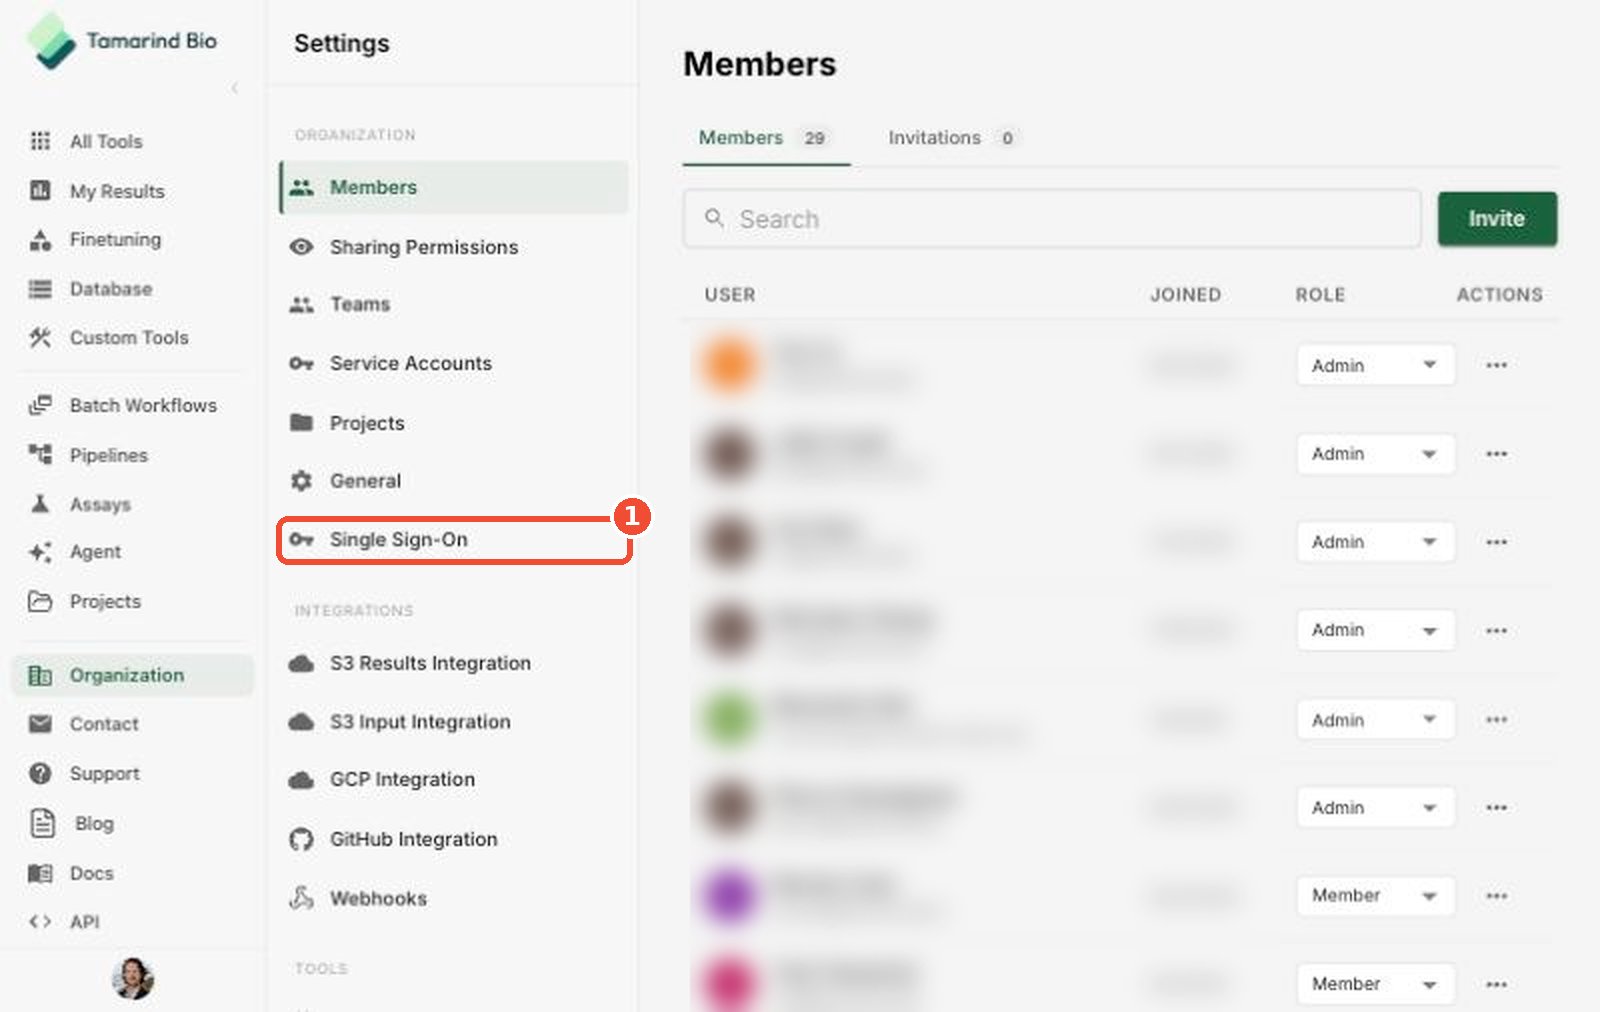
3. Choose your identity provider and email domain
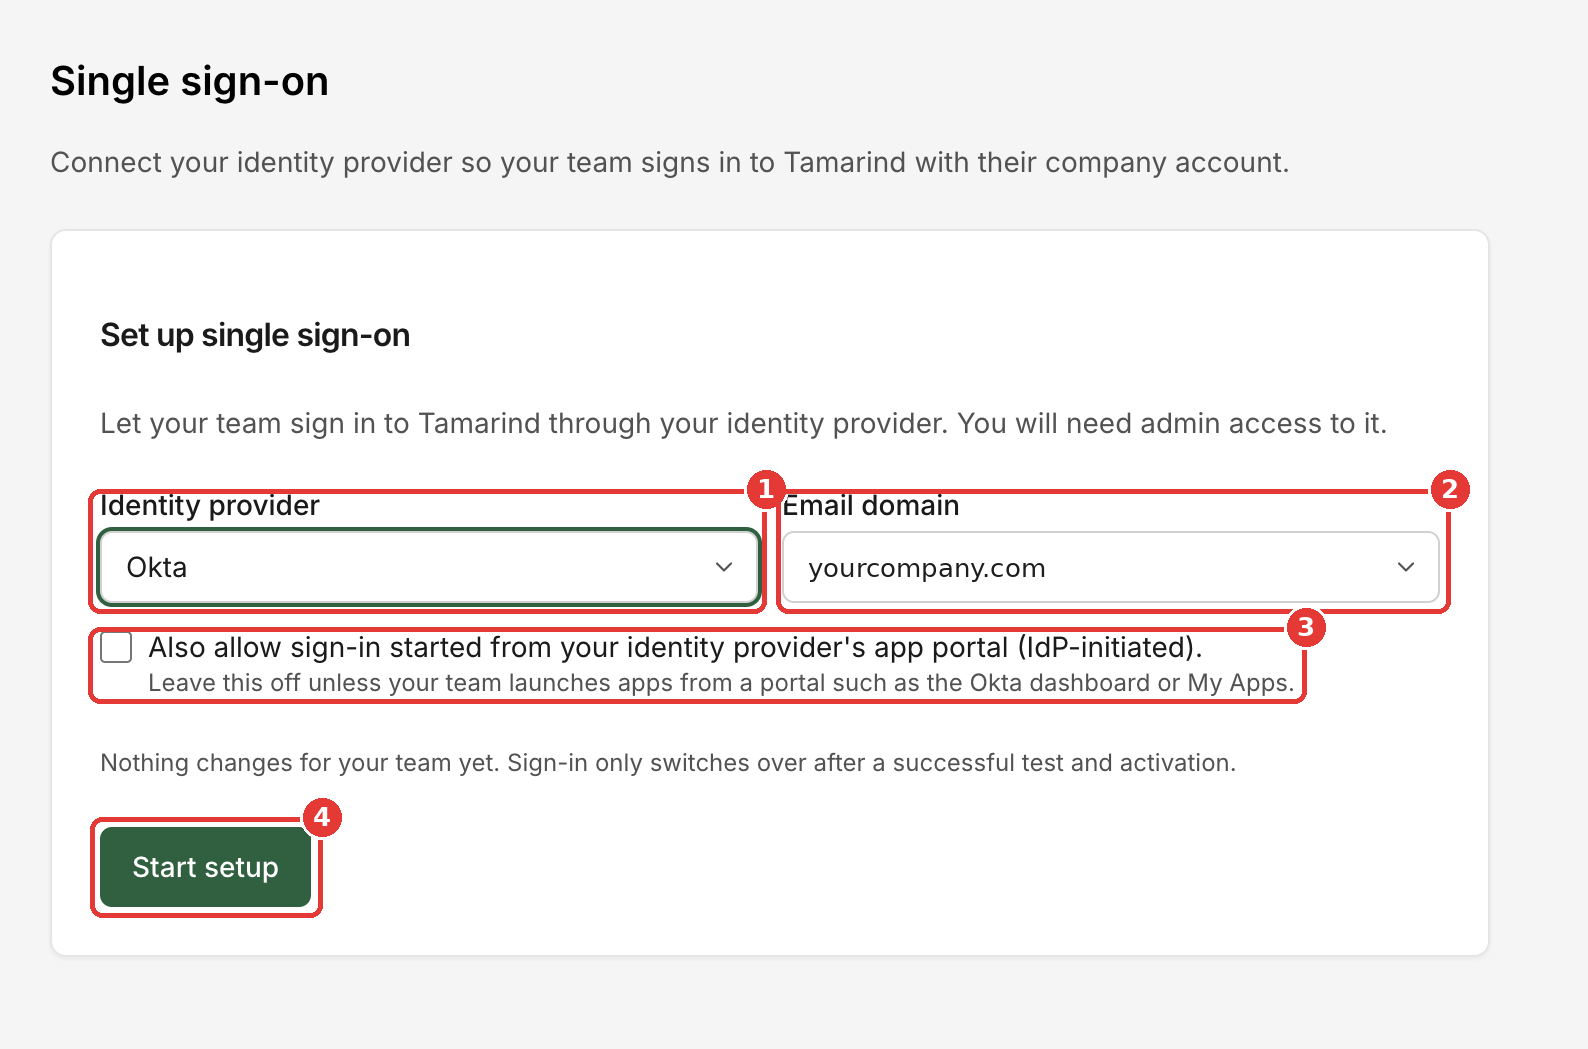
Under Set up single sign-on:-
Identity provider — select the provider your company uses:
The setup steps on the next screen are written for the provider you pick.
- Email domain — select the company email domain that should sign in through SSO. Everyone with an email on this domain will use SSO once it’s activated.
- IdP-initiated sign-in (optional) — check this only if your team launches apps from a portal such as the Okta dashboard or Microsoft My Apps. Leave it off otherwise. You can change this later.
- Click Start setup.
If you see “Your organization already has a single sign-on connection that Tamarind set up for you,” your SSO is managed by Tamarind. Contact us to make changes.
4. Review your SSO connection
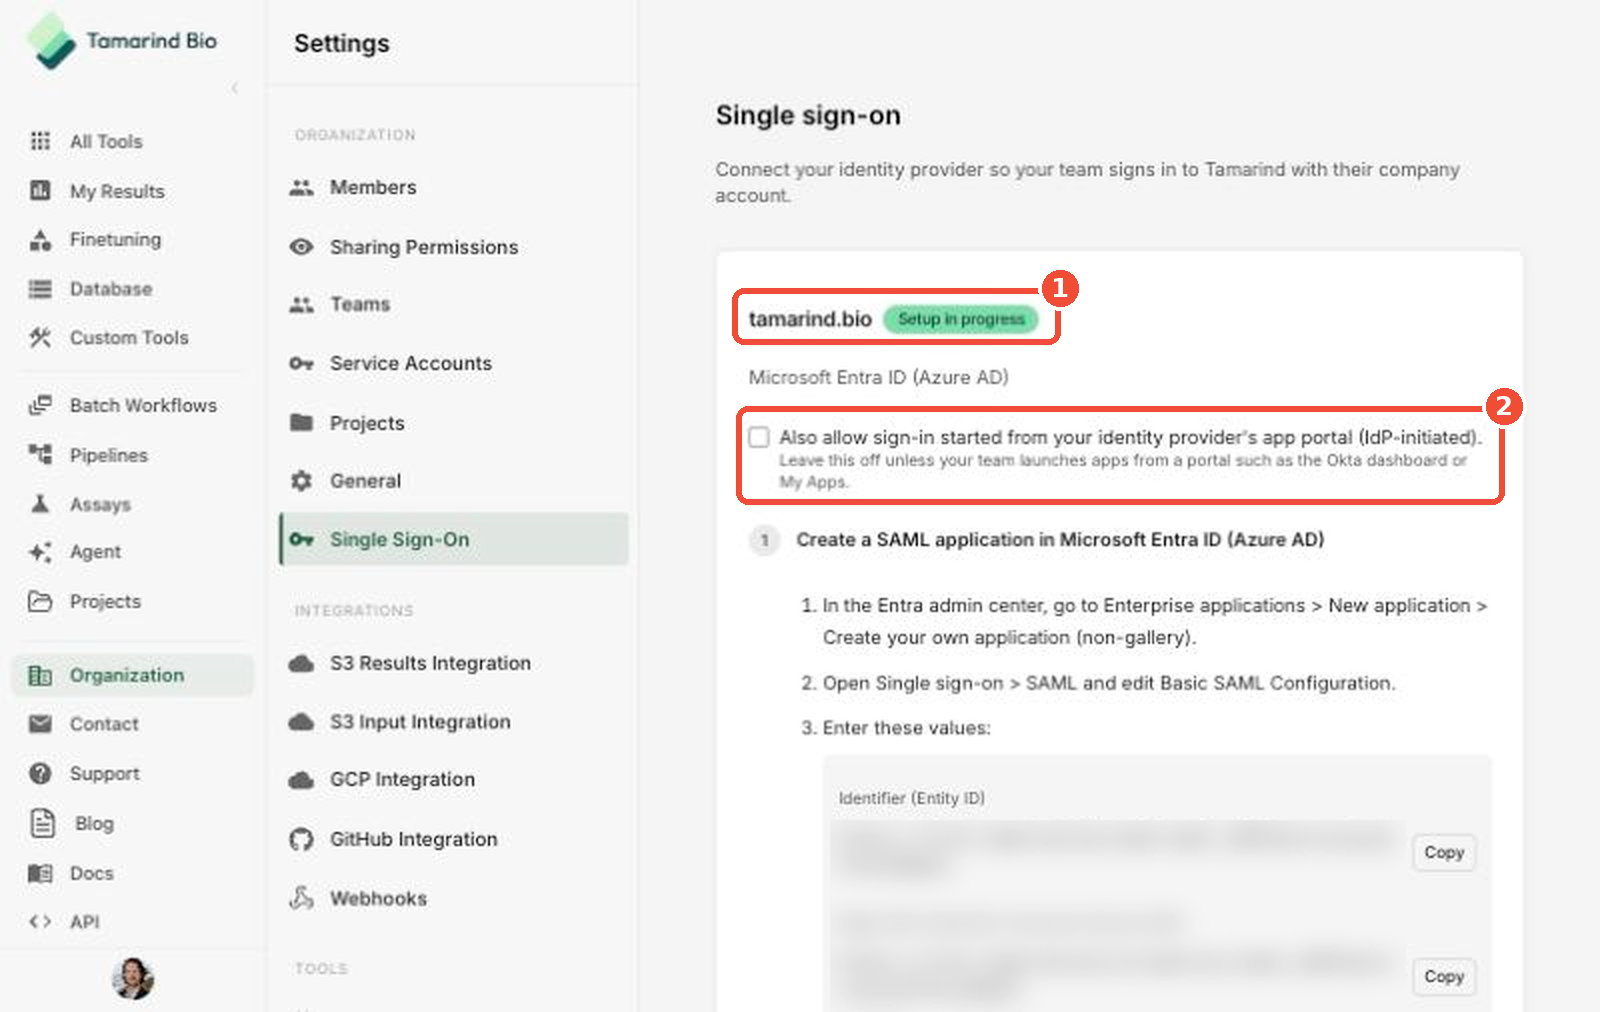
After you click Start setup, the page shows your connection:- Your domain and status — for example,
yourcompany.comwith a Setup in progress badge. - IdP-initiated sign-in — the same option from Step 3, which you can still change here.
5. Create a SAML application in your identity provider
Tamarind shows the values your IdP needs, such as the Entity ID and Assertion Consumer Service (ACS) URL, with Copy buttons (1).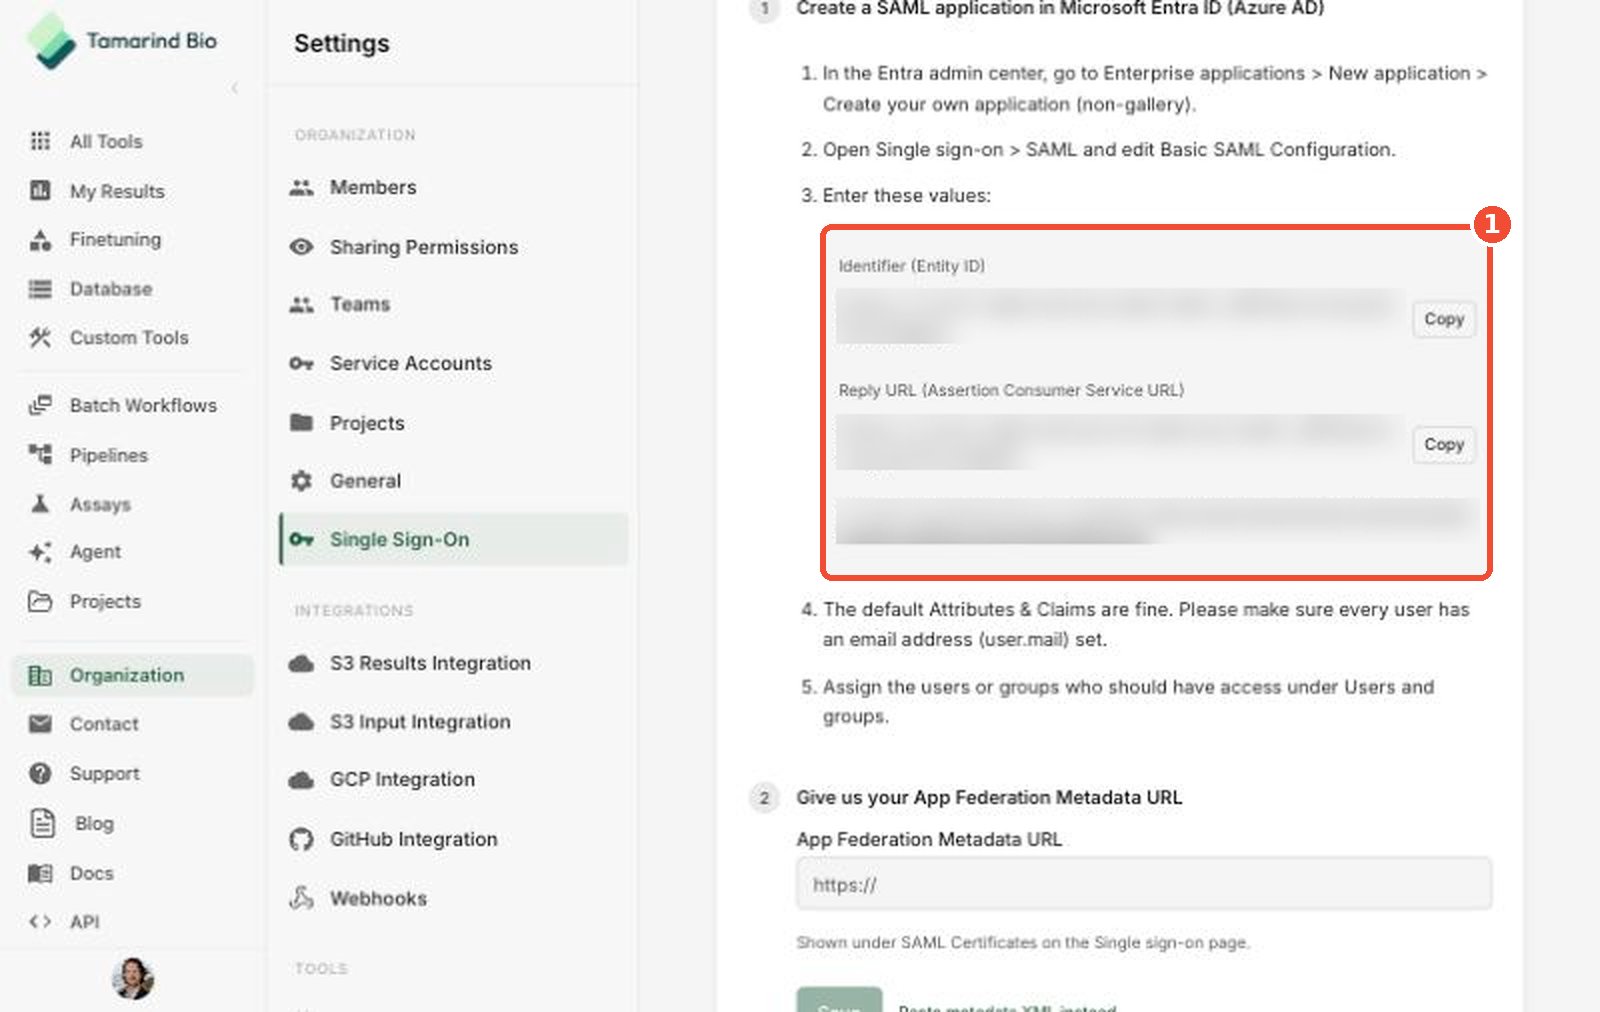
These values are unique to your organization. Always copy them from your own Tamarind SSO page.
Microsoft Entra ID
- In the Entra admin center, go to Enterprise applications → New application → Create your own application (non-gallery).
- Open Single sign-on → SAML and edit Basic SAML Configuration.
-
Paste the values from Tamarind:
Or, import everything at once using the metadata URL shown below the two values.
-
Keep the default Attributes & Claims. Make sure every user has an email address (
user.mail) set. - Under Users and groups, assign the users or groups who should have access to Tamarind.
Okta
- In the Okta Admin Console, go to Applications → Applications → Create App Integration, then choose SAML 2.0.
- Name the app (for example, Tamarind Bio) and continue to Configure SAML.
- Paste the Tamarind ACS URL into Single sign-on URL and the Entity ID into Audience URI (SP Entity ID).
- Set Name ID format to EmailAddress and Application username to Email.
- Finish the wizard, then assign users or groups on the app’s Assignments tab.
Google Workspace
- In the Google Admin console, go to Apps → Web and mobile apps → Add app → Add custom SAML app.
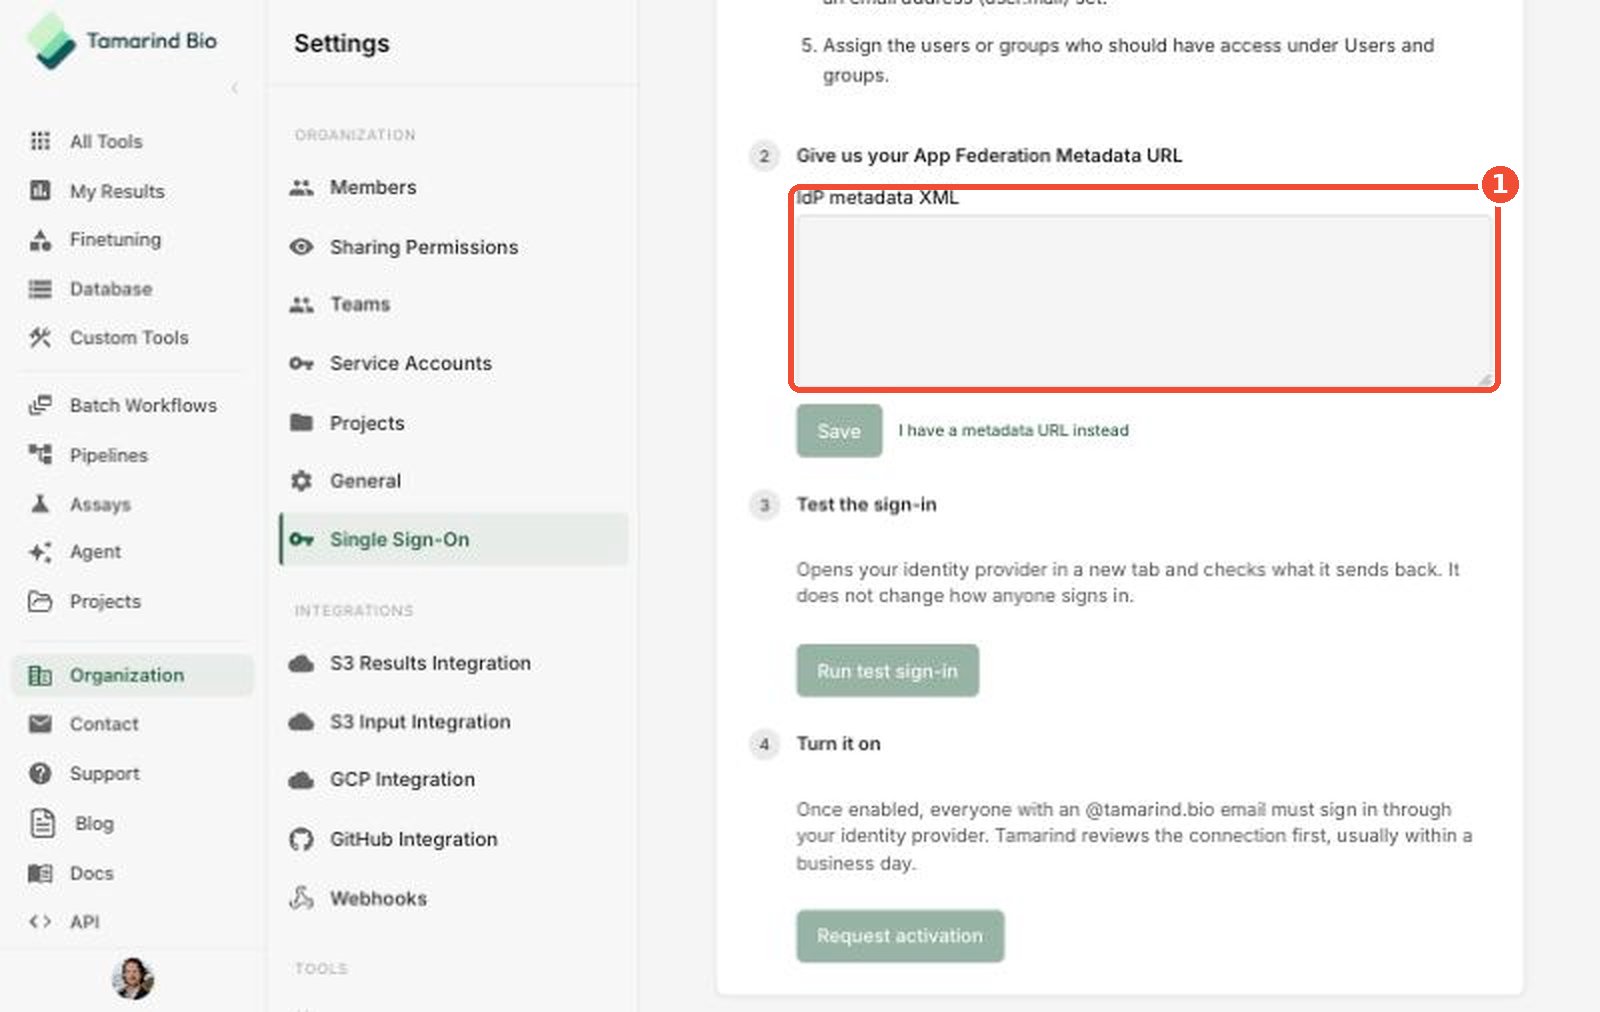
- Name the app (for example, Tamarind Bio) and continue. On the Google Identity Provider details screen, click Download metadata — you’ll give this file to Tamarind in Step 6.
- Paste the Tamarind ACS URL and Entity ID into the matching fields.
- Set Name ID format to EMAIL and Name ID to Basic Information > Primary email.
- Finish, then turn the app ON for the organizational units or groups who should have access.
Other SAML provider
Create a new SAML 2.0 application in your IdP and configure:- ACS URL / Reply URL / Single sign-on URL: the Tamarind ACS URL
- Entity ID / Audience: the Tamarind Entity ID
- Name ID: the user’s email address
6. Connect, test, and activate
Give Tamarind your IdP metadata
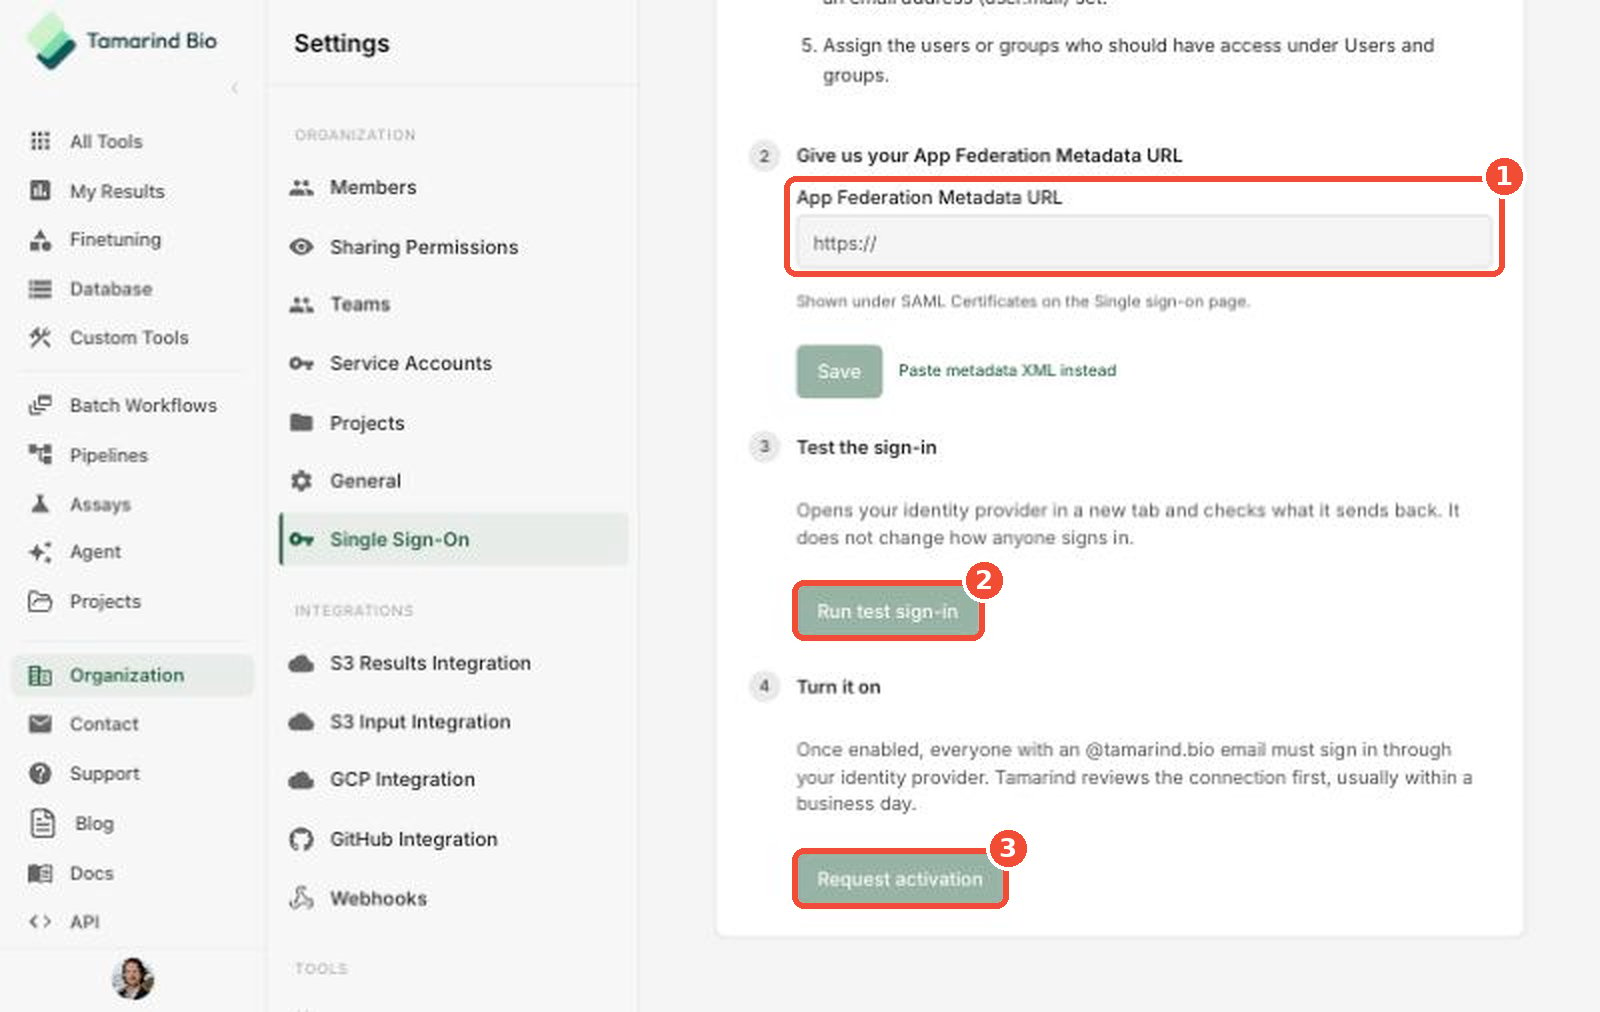
Paste your IdP’s metadata URL into the metadata URL field (1) and click Save.